Responsible AI Consulting Services in the San Francisco Bay Area: What They Do and How to Choose One
Responsible AI Consulting Services in the Bay Area: The Short Version
Key takeaway: Responsible AI consulting services help San Francisco Bay Area companies build AI systems that are safe, fair, and compliant with emerging rules. Typical engagements cover AI risk assessments, governance policies, bias testing, and EU AI Act or ISO 42001 readiness. Options range from large professional-services practices to boutique specialists — choose based on independence, framework expertise, and relevant references.
If you are building or buying AI in the San Francisco Bay Area, responsible AI consulting services are the outside experts companies hire to make sure their AI systems do not cause harm, create legal exposure, or quietly discriminate. They are part strategist, part auditor, and part translator between your engineering team and the fast-moving world of AI regulation. With the EU AI Act’s obligations phasing in through 2026 and enterprise buyers increasingly demanding proof of AI governance, demand for these services in the Bay Area — home to many of the world’s largest AI labs and a dense cluster of AI startups — has grown sharply.
What Responsible AI Consulting Services Actually Do
At their core, these firms help organizations answer one question: do we know what our AI systems are doing, and can we prove it? Their work typically breaks into four areas:
- AI risk assessment. Mapping every AI system a company uses or sells, documenting what each one does, who it affects, and where the risks sit. This mirrors the Map and Measure functions of the NIST AI Risk Management Framework (AI RMF 1.0), the voluntary U.S. guidance published in January 2023 and built around four functions — Govern, Map, Measure, and Manage (framework reference).
- Governance design. Writing the policies, roles, and approval gates that decide who can ship an AI feature and under what conditions — the Govern function in NIST terms.
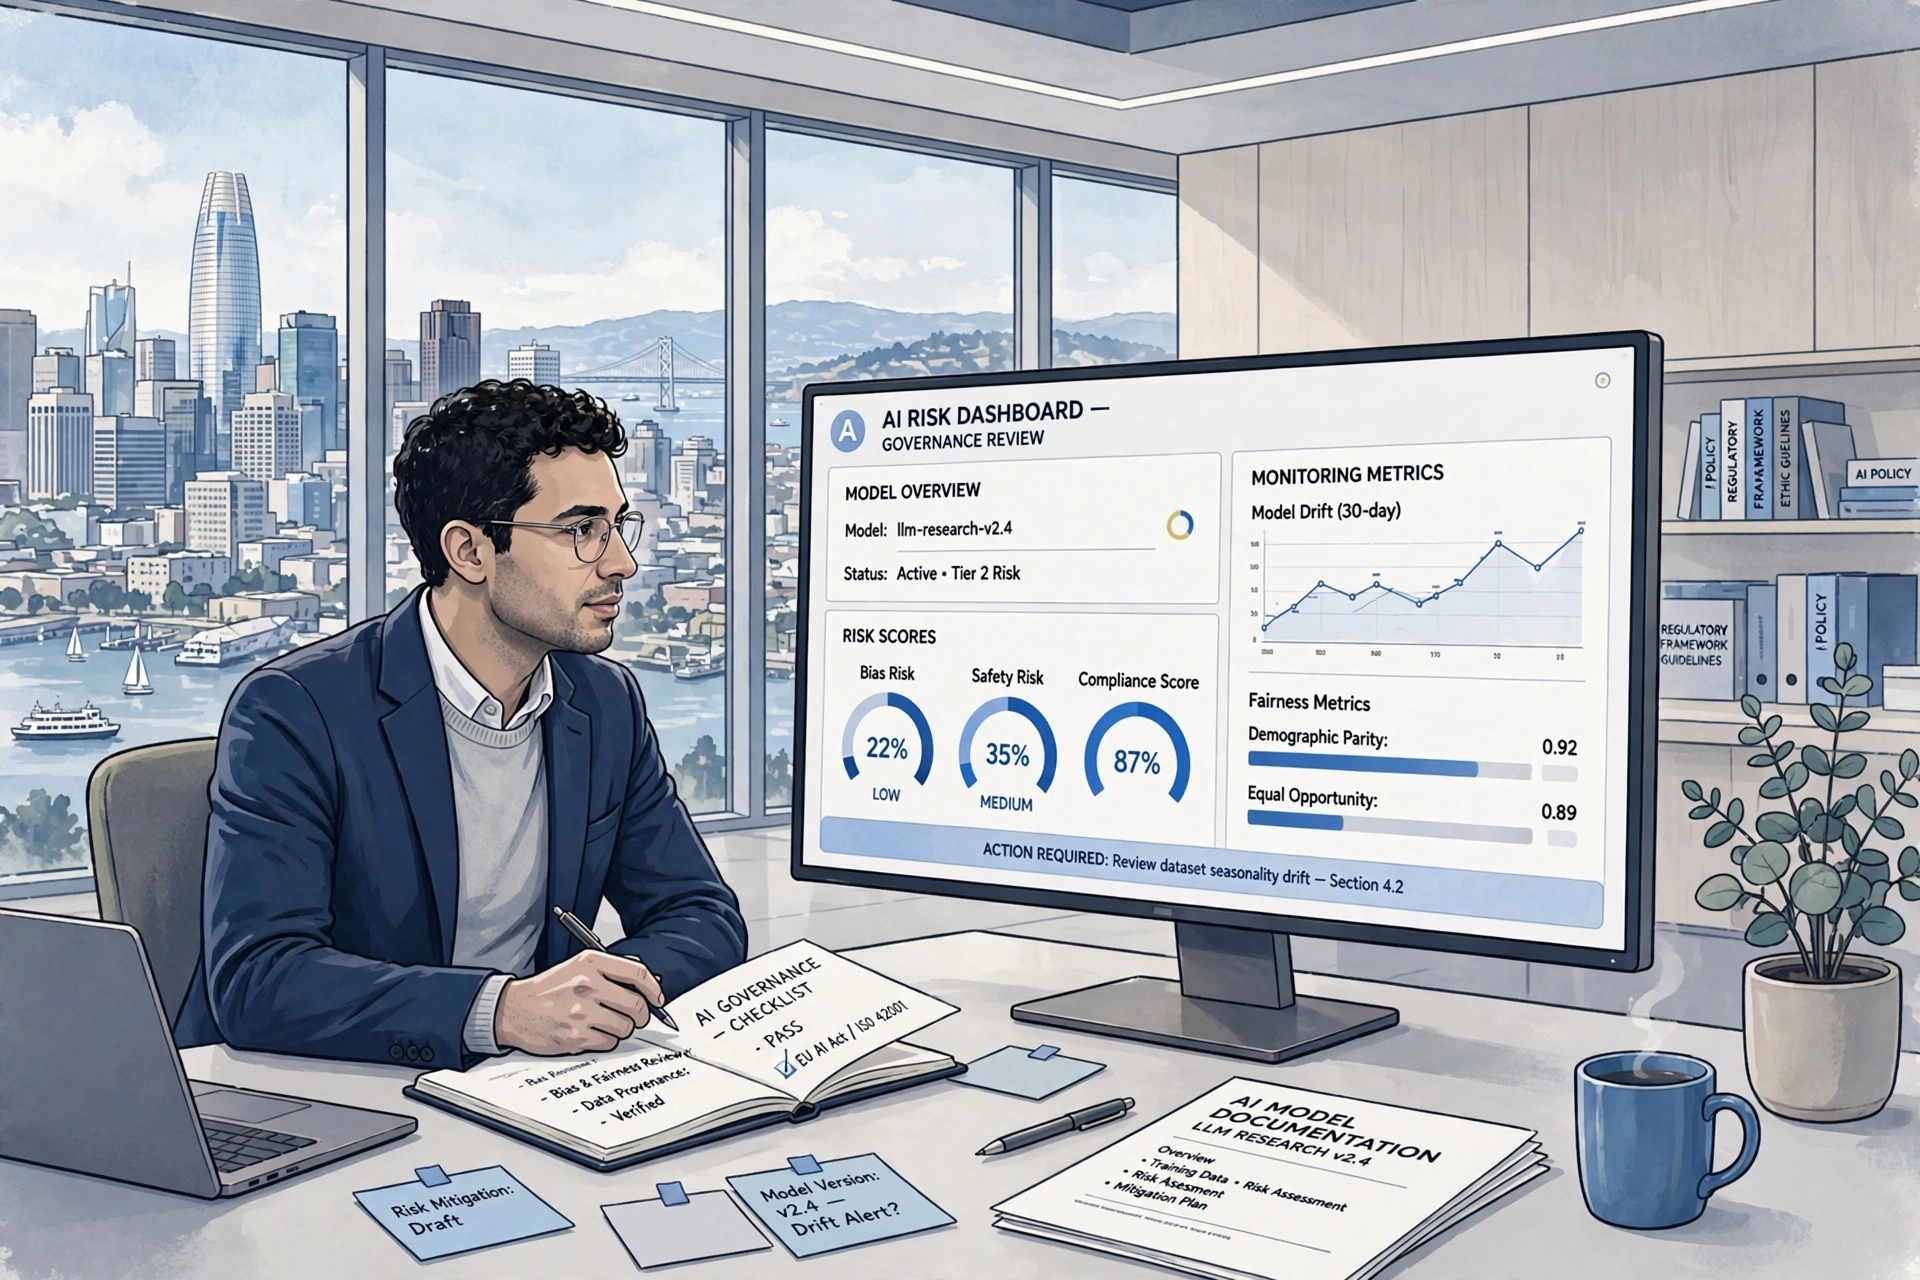
- Testing and evaluation. Bias and fairness testing across demographic groups, red-teaming of generative AI systems, and monitoring for model drift in production.
- Compliance readiness. Mapping a company’s practices to specific legal duties — most notably the EU AI Act, whose obligations for general-purpose AI models have applied since August 2, 2025 (EU AI Act implementation timeline), and ISO/IEC 42001, the international AI management system standard published in December 2023 (certification guide).
Why Bay Area Companies Are Hiring Them Now
Three forces are converging on the region’s AI companies at once. First, the EU AI Act applies based on where an AI system’s outputs are used, not where the company is headquartered — so Bay Area firms selling into Europe are in scope regardless of their location. The Act’s high-risk system obligations were originally set for August 2026, though a July 2026 Digital Omnibus package proposed moving Annex III deadlines out; transparency rules and general-purpose model duties are already live, with fines for the most serious violations reaching up to €35 million or 7% of global turnover.
Second, enterprise procurement is doing the regulators’ work for them. Large buyers increasingly ask AI vendors for evidence of responsible AI management before signing — and ISO/IEC 42001 certification, awarded by independent certification bodies after a two-stage audit, has become the recognized benchmark (how certification works). Third, many startups simply cannot staff a full governance team: a consultant who has mapped NIST’s framework to a dozen companies can stand up a program in weeks that would take a lone hire a year to build.
What Is Usually Included in an Engagement
Engagements vary in size, but a typical responsible AI consulting project in the Bay Area includes:
- AI system inventory — a documented list of every model, dataset, and third-party AI service in use, with owners and risk tiers.
- Risk and impact assessment — structured evaluation of each system against harm categories such as bias, safety, security, and privacy.
- Governance documentation — acceptable-use policies, model review processes, incident response plans, and an AI literacy training program (the EU AI Act has required AI literacy measures since February 2025).
- Bias and robustness testing — disaggregated performance metrics and adversarial testing of high-impact systems.
- Compliance gap analysis — a mapping of current practices against the EU AI Act, NIST AI RMF, and/or ISO 42001, with a prioritized remediation roadmap.
- Certification prep — for companies pursuing ISO 42001, preparing the AI management system (AIMS) documentation and controls ahead of the certification audit.
How to Choose the Right Responsible AI Consulting Firm
Not all consultants are equal. Ask these questions before signing:
- Are they independent? A firm that also sells the AI models or platforms it audits has a built-in conflict of interest. Independence is what makes the findings credible to your buyers and regulators.
- Which frameworks do they work in? Look for hands-on experience with NIST AI RMF, ISO/IEC 42001, and the EU AI Act — not just name-dropping. Ask for a sample deliverable (redacted) from a past engagement.
- Do they understand your AI stack? A consultant who has only worked with traditional machine learning will struggle with agentic AI or LLM-specific risks like data leakage and prompt injection. Match their experience to your systems.
- Who will actually do the work? Boutique firms often give you the partner; large practices sometimes hand off to junior staff. Ask for the engagement team’s names and backgrounds.
- What does “done” look like? Insist on a defined scope — risk register, policy documents, testing reports — rather than open-ended advisory hours.
Our Analysis: What to Watch in 2026
Analysis, not verified fact: The Bay Area’s responsible AI consulting market is likely to split into two tiers — certification-oriented firms competing on ISO 42001 audit readiness, and litigation-oriented practices focused on EU AI Act enforcement defense. Our read: companies that treat this as a checkbox exercise will pay twice — once for the paperwork, and again when a buyer or regulator asks for evidence the paperwork describes. The firms worth hiring are the ones whose deliverables your engineering team would actually use.
For background on building AI responsibility into your products from the start, see our explainers on achieving responsible AI with the SAFE approach, AI-first engineering, and the intelligent business automation whitepaper.
Frequently Asked Questions
What does a responsible AI consulting firm actually do?
A responsible AI consulting firm assesses the risks of your AI systems, designs governance policies and controls, tests models for bias and safety, and prepares you for compliance with frameworks like the EU AI Act, NIST AI RMF, and ISO/IEC 42001. Typical deliverables include a risk register, policy documentation, testing reports, and a remediation roadmap.
When should a company hire one instead of building an in-house team?
Hire consultants when you need speed, independence, or expertise you do not have in-house — for example, ahead of an ISO 42001 certification audit, before launching a high-risk AI product in Europe, or when enterprise buyers ask for governance evidence. Build in-house when AI governance becomes an ongoing, full-time function, often after the consultants have set up the initial program.
How do these services relate to the EU AI Act and ISO/IEC 42001?
Consultants map your current practices against these frameworks and close the gaps. For the EU AI Act, that means duties like risk management, documentation, transparency, and AI literacy that have been phasing in since February 2025. For ISO/IEC 42001, it means building an AI management system that can pass a third-party certification audit.
How much do responsible AI consulting services cost?
Fees vary widely with scope. A focused risk assessment for a single AI product costs far less than a multi-month program covering ISO 42001 certification readiness across an enterprise. Always get a fixed scope with defined deliverables rather than open-ended hourly billing, and ask for references from companies of a similar size and AI maturity.
Sources
- NIST AI RMF 1.0 reference — four functions (Govern, Map, Measure, Manage), published January 2023
- ISO 42001 certification guide — standard published December 2023, third-party certification model
- ISO/IEC 42001 AI management system overview — two-stage audit, three-year certificate validity
- EU AI Act implementation timeline (European Commission AI Act Service Desk)