Top Strategies for Aligning AI Initiatives with Ethical Standards in 2026
Key takeaway: Aligning AI initiatives with ethical standards means building governance into every stage of an AI project: choosing a recognised framework, mapping each system against the law, testing for bias, and keeping a human accountable for decisions. With EU AI Act enforcement now live, it is a legal necessity as well as good practice.
Every company using AI now faces the same question: how do you move fast without building something unfair, unsafe, or illegal? The top strategies for aligning AI initiatives with ethical standards below are drawn from frameworks and rules already in force in 2026 — NIST’s AI Risk Management Framework, the EU AI Act, and working governance programmes at companies like IBM.
What “aligning AI with ethical standards” actually means
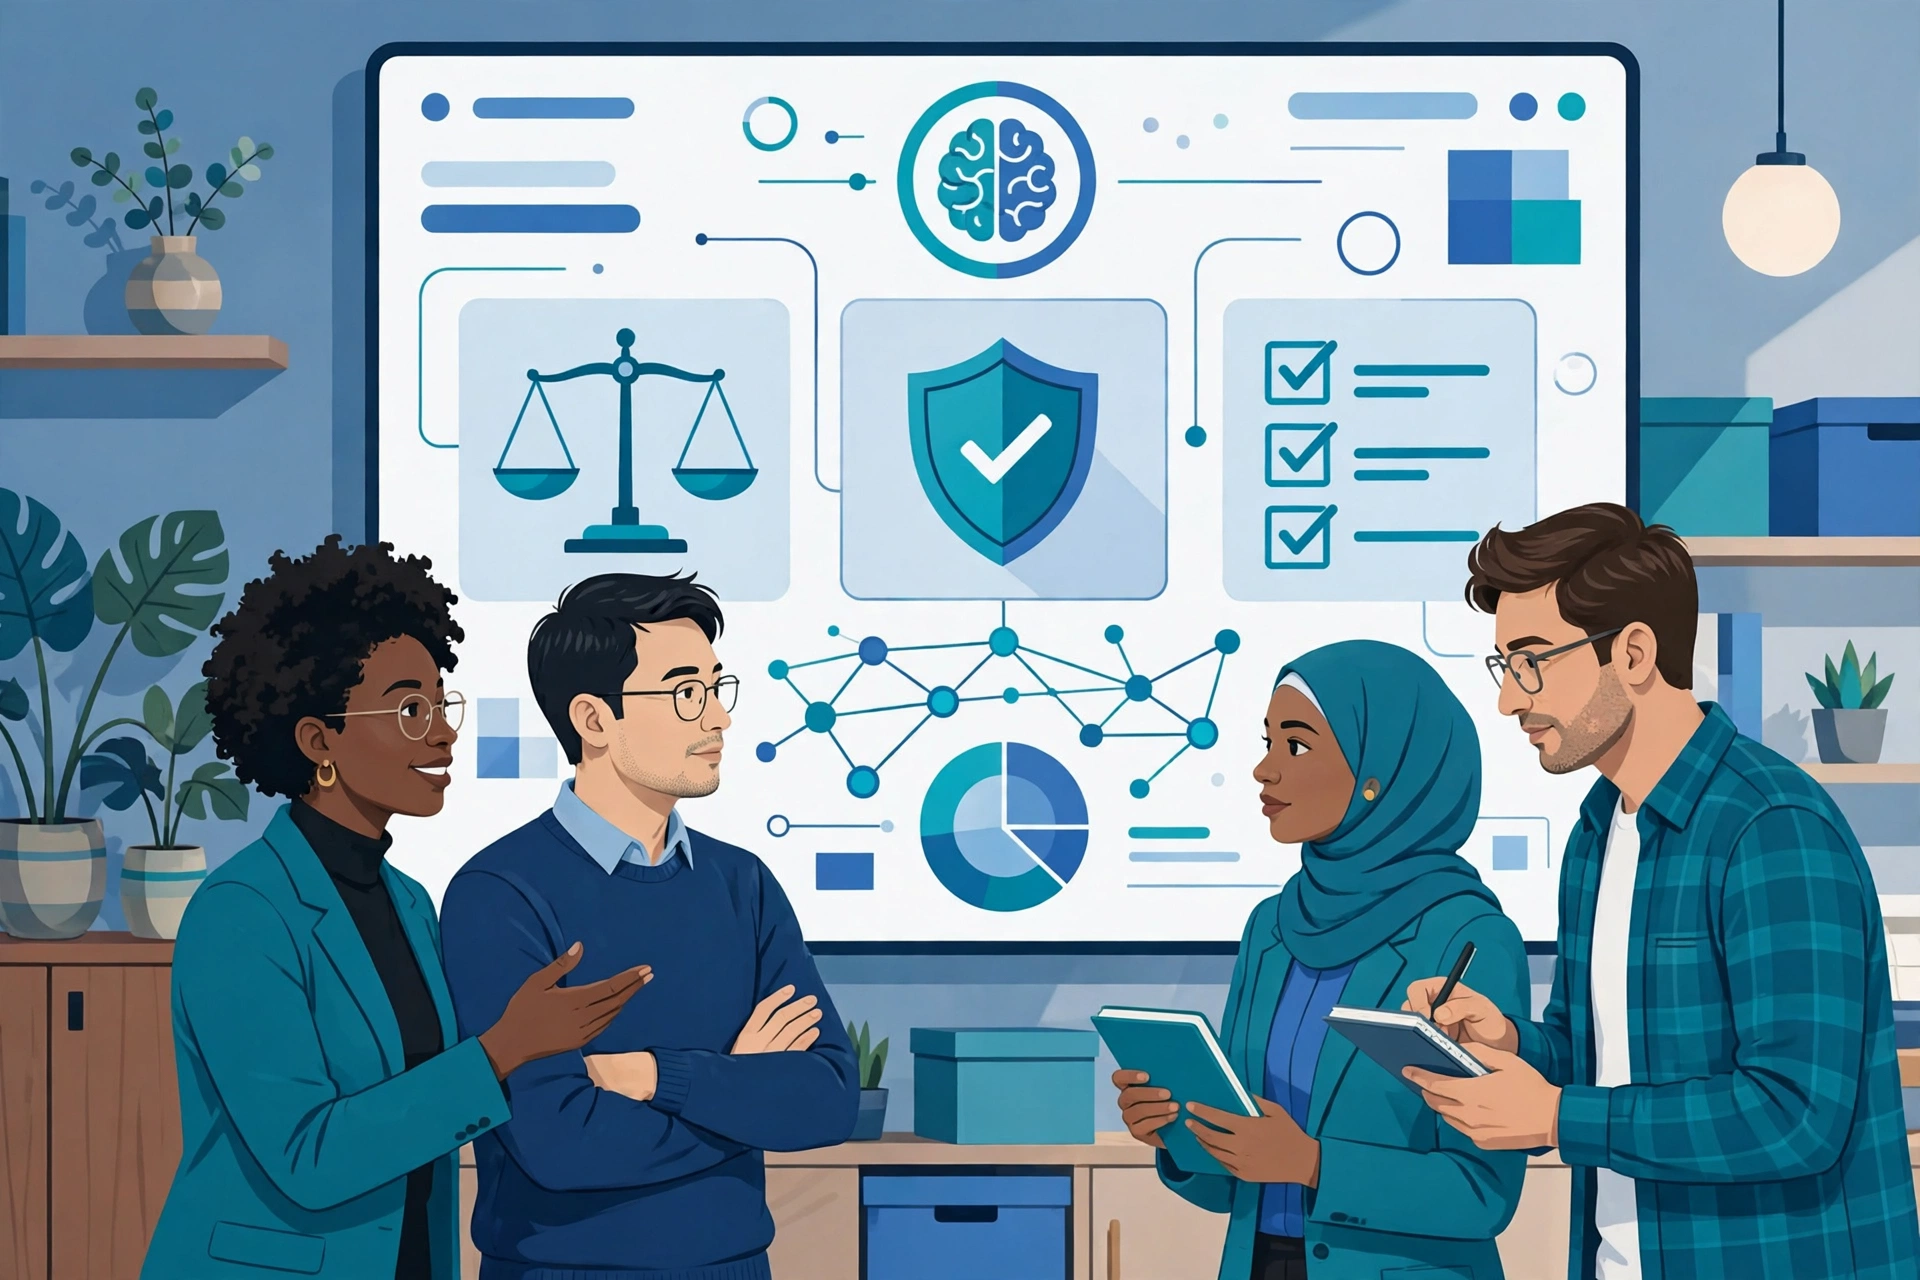
Alignment is not a mission statement on a wall. In practice it means an AI system is fair, transparent, explainable, and accountable — a named person owns the outcome. IBM builds its programme around those same qualities, plus robustness and privacy, as its five Pillars of Trust.
Top strategies for aligning AI initiatives with ethical standards
1. Adopt a recognised framework instead of inventing your own
The fastest credible starting point is the NIST AI Risk Management Framework (AI RMF 1.0), released on January 26, 2023. Built with input from more than 240 organisations, it organises risk work into four functions: Govern, Map, Measure, and Manage. NIST added a Generative AI Profile (NIST AI 600-1) in July 2024. It also pays off legally: Texas’s AI law (TRAIGA), effective January 1, 2026, gives organisations an affirmative defence if they substantially comply with the NIST AI RMF Generative AI Profile or a similar recognised framework.
2. Map every AI system against the law that applies to it
Frameworks guide you; laws bind you. Under the EU AI Act, obligations for general-purpose AI (GPAI) model providers have applied since August 2, 2025, and the European Commission’s power to enforce them — fines up to 3% of worldwide annual turnover or €15 million — went live on August 2, 2026. High-risk systems, such as AI used in hiring or credit decisions, were pushed back by the Digital Omnibus to December 2, 2027. Map each system to its tier before you build, not after. For a plain-English primer on why governance now drives AI projects, see our earlier piece on why AI transformation is a problem of governance, not technology.
3. Test for bias before launch — and keep testing after
Bias testing is where ethics stops being theory. A Harvard Business Review study cited by IBM found 79% of senior IT leaders worry generative AI brings security risks, and 73% worry about biased outcomes. Test training data for representation gaps and model outputs across demographic groups, then repeat the tests after deployment, because models drift. IBM open-sourced tooling for this: AI Fairness 360 for bias metrics and AI Explainability 360 for explaining decisions.
4. Keep a human accountable for decisions
IBM’s first principle for trustworthy AI, in place since 2018, is that AI should augment human intelligence, not replace it — and a human stays responsible for decisions even when an AI system supports them. In practice: a named owner for every AI system, human review of high-stakes outputs, and a clear escalation path when the system is wrong. This matters most where AI touches people directly — hiring, lending, safety, healthcare — as our guide to how safety teams use AI shows.
5. Monitor, audit, and document continuously
Alignment is not a launch-day checkbox. Log how systems behave in production, watch for drift and new failure modes, run periodic audits, and keep documentation that reads like a nutrition label for each model — IBM’s AI FactSheets template covers how a model was built, tested, and intended to be used. Practitioners warn a credible programme takes about a year to build, starting with governance and an inventory, not technical testing.
Framework comparison: NIST AI RMF vs ISO/IEC 42001 vs the EU AI Act
| Framework | What it is | Binding? | Best for |
|---|---|---|---|
| NIST AI RMF 1.0 | Voluntary risk framework; Govern, Map, Measure, Manage | No | Any organisation starting AI governance |
| ISO/IEC 42001 | Certifiable AI management-system standard | No — certification is voluntary | Organisations wanting audited governance |
| EU AI Act | EU law with risk tiers and fines | Yes, for the EU market | Any company offering AI in the EU |
Most organisations combine them: NIST AI RMF for the working method, ISO/IEC 42001 where certification helps with customers, and the EU AI Act as the legal floor.
What it costs — and what skipping it costs
A governance programme costs staff time, tooling, and audits, and practitioners put a credible programme at roughly a year to build. Skipping it costs more: the EU AI Act allows fines of up to €35 million or 7% of global annual turnover for the most serious violations. Beyond fines, a biased hiring tool or an unexplained loan denial brings reputational damage and lawsuits no policy document can undo. And doing nothing is not a safe option — companies that avoid AI entirely are already falling behind competitors. The choice is between governed AI and ungoverned AI.
Risks and limits
Three honest limits. First, adopting a framework does not make you compliant: the AI RMF is voluntary guidance and does not by itself satisfy the EU AI Act, HIPAA, or a state automated-decision law. Second, alignment, compliance, and risk reduction are three different things — the real risk management is the bias testing, red-teaming, monitoring, and human review. Third, NIST is revising the AI RMF under the White House AI Action Plan, so programmes should expect wording changes.
Our take
Analysis: The cheapest moment to align an AI initiative with ethical standards is before the first model ships. Start with the NIST AI RMF’s Govern function — a named owner, a written policy, and an inventory of what you already run — then map the legal tier of each system, then test.
Frequently asked questions
What does it mean to align AI initiatives with ethical standards?
It means building AI systems so they are fair, transparent, explainable, and accountable at every stage — from choosing training data to monitoring the system after launch. It is done through a recognised framework, written policies, bias testing, and a named human owner for each system.
Which framework should a company start with?
Most organisations start with the NIST AI Risk Management Framework (AI RMF 1.0), a voluntary framework released in January 2023 that organises AI risk work into four functions: Govern, Map, Measure, and Manage. Its Generative AI Profile covers generative models specifically.
Does following the NIST AI RMF make a company compliant with the EU AI Act?
No. The AI RMF is voluntary guidance, and adopting it does not by itself satisfy the EU AI Act or other laws. It can help structure a compliance programme, but each law carries its own requirements that must be met separately.
What are the EU AI Act deadlines companies should know in 2026?
GPAI model obligations have applied since August 2, 2025, and the European Commission’s enforcement powers, including fines of up to 3% of worldwide turnover or €15 million, went live on August 2, 2026. High-risk system obligations were deferred to December 2, 2027 by the Digital Omnibus.
How can a small team test AI for bias without a big budget?
Start with free, open-source tooling such as IBM’s AI Fairness 360 for bias metrics and AI Explainability 360 for explaining decisions. Test training data for representation gaps, test outputs across demographic groups, repeat tests after deployment, and record the results.
Sources
- NIST AI Risk Management Framework (AI RMF 1.0) — framework overview, January 26, 2023 release, Generative AI Profile (NIST AI 600-1, July 2024)
- IBM — Guide for Implementing an AI Governance Framework — governance steps, HBR survey figures, EU AI Act penalties
- IBM — AI Best Practices — Principles for Trust and Transparency, five Pillars of Trust
- Taylor Wessing — GPAI obligations under the EU AI Act — enforcement from August 2, 2026, Digital Omnibus deferrals
- AI Policy Desk — EU AI Act GPAI Compliance Checklist — timeline and fine levels
- Ampcus Cyber — NIST CSF 2.0 and AI RMF Implementation Guide — Texas TRAIGA affirmative defence, AI RMF functions