Cybersecurity Automation Tools for Enterprise SOCs Explained: SOAR, Playbooks, and How to Choose
Key takeaway: Cybersecurity automation tools for enterprise SOCs connect the security tools a team already owns, enrich alerts with context, and run repeatable response playbooks — so analysts spend less time on copy-paste triage and more on real threats. The best choice usually follows the stack you already run, not the longest feature list.
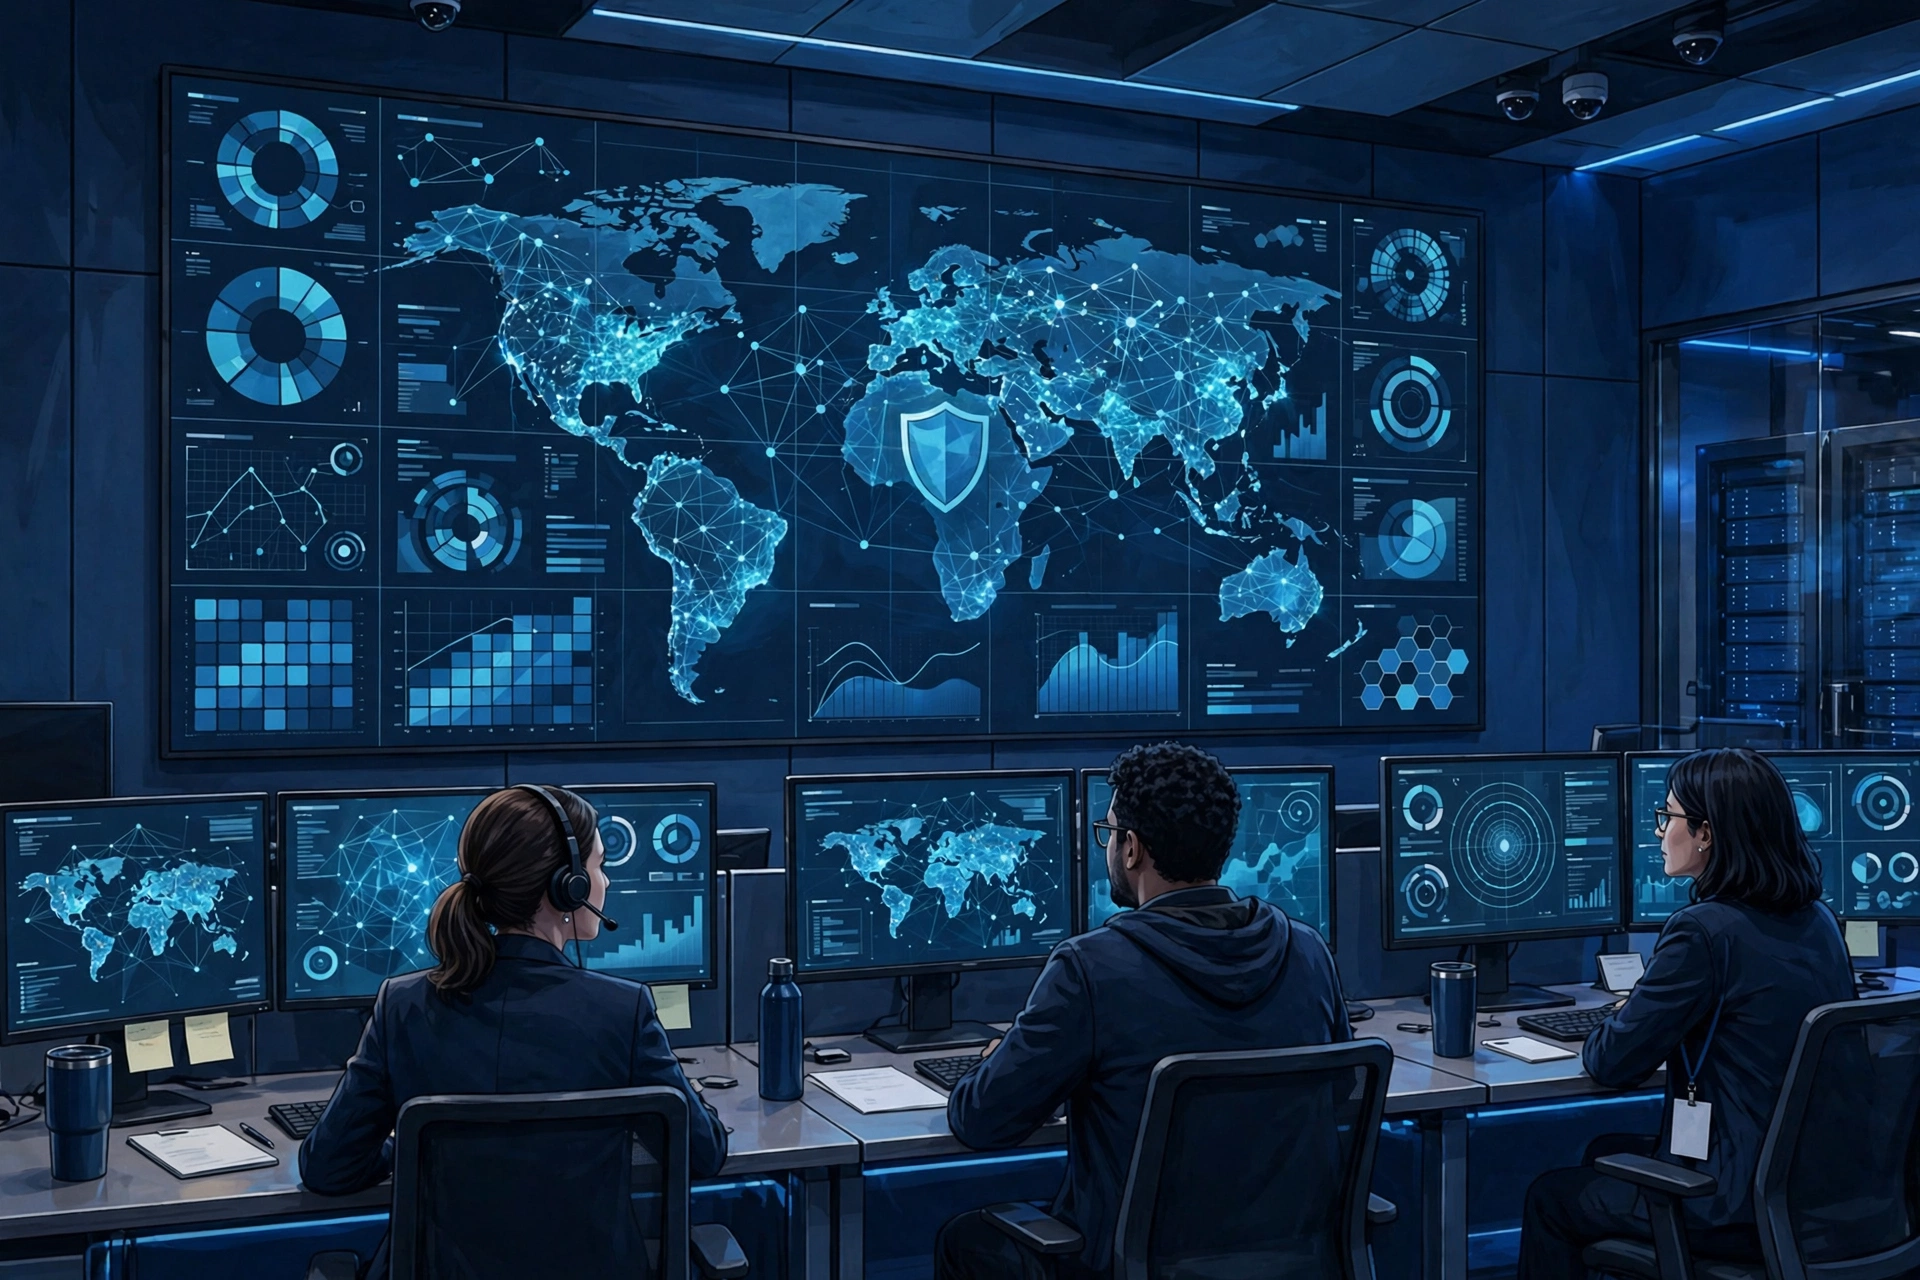
An enterprise security operations center (SOC) can receive thousands of alerts a day from firewalls, endpoint agents, cloud platforms, identity systems, and email gateways. No team can investigate each one by hand at that volume. That is the problem cybersecurity automation tools are built to solve: they sit above detection tools and decide what happens next, in seconds, the same way every time.
The core category is SOAR — security orchestration, automation, and response. The term was coined by Gartner around 2015, and it describes platforms that integrate security tools, automate repetitive tasks, and standardize incident response, as Comparitech’s SOAR guide explains. Put simply: a SIEM tells you something looks wrong; SOAR decides what happens next.
What cybersecurity automation tools for enterprise SOCs actually do
When an alert arrives, a SOAR platform can pull the user’s login history, check a file hash against threat-intelligence feeds, look up the asset owner, and open a ticket with all of that evidence attached. Done manually, those steps might take an analyst 20 minutes. Automated, they take seconds — and every analyst gets the same evidence, in the same order.
The instructions behind this are called playbooks: a written response process turned into steps a machine can run. They typically cover enrichment (adding context to a bare alert), triage (closing known false positives automatically, with an evidence trail), and containment (blocking an IP or isolating an endpoint, often only after human approval). Microsoft documents the same pattern for Sentinel, where playbooks built on Azure Logic Apps run automatically through an automation rule or manually on a specific incident, per Microsoft Learn. Palo Alto documents a similar model for Cortex XSOAR, where playbooks enrich indicators, update severity, and optionally trigger firewall remediation, per its Cortex XDR documentation.
Why it matters: alert volume rises, headcount does not
The payoff is measured in mean time to detect (MTTD) and mean time to respond (MTTR). Automated triage compresses the gap between an alert firing and a first response, and consistent playbooks mean a critical check is not skipped just because the queue is busy at 3 a.m. The pressure is real: attackers use automation too — Cisco Talos found the VOLTA infostealer handing stolen data to AI to rank victims, and Chainalysis disclosed a breach carried out with offensive agentic techniques. A SOC triaging by hand competes against automated attackers with a manual process.
Cybersecurity automation tools compared
No single tool wins for every SOC, because the right choice depends heavily on what the team already runs:
| Platform | Build model | Best stack fit | Standout strength |
|---|---|---|---|
| Palo Alto Cortex XSOAR | Playbook and code | Palo Alto, or stack-neutral | Deepest playbook library and integration marketplace |
| Splunk SOAR | Visual and code playbooks | Teams standardized on Splunk | Automation fused into the Splunk Enterprise Security workflow |
| Microsoft Sentinel (Logic Apps) | Logic Apps workflows | Microsoft-centric estates | Bundled SIEM plus automation; consumption-based pricing |
| Tines / Torq | No-code builders | Stack-neutral teams | Fastest time from idea to running workflow |
A 2026 editorial ranking by CybersecurityNews put Cortex XSOAR first for playbook depth, Splunk SOAR second for SIEM-fused automation, and Tines third for no-code build speed — explicitly research-based, not lab-tested. Treat any ranking as a shortlist: run your own top three playbooks against each finalist before buying.
How much do cybersecurity automation tools cost?
There is no honest single price. Enterprise SOAR platforms are usually quote-based, priced on analyst seats, event volume, or both, so budget for licensing plus implementation and ongoing playbook maintenance — not just the license. Sentinel works differently: it is priced largely on data ingested, and its Logic Apps playbooks can add consumption charges, which Microsoft Learn flags directly. The cost buyers most often underestimate is upkeep: integrations break when vendors change APIs, and a platform bought without a named owner and maintenance time tends to become expensive shelfware.
What a SOC needs before automation pays off
Automation multiplies whatever detection quality already exists; it does not fix it. Before buying, a SOC should have logs actually flowing into the SIEM from endpoints, identity, cloud, and network; documented response processes that can be encoded; a named engineer who owns playbooks as an ongoing job; and approval gates for risky actions like disabling accounts. One timing detail for Microsoft shops: Microsoft says Sentinel will no longer be supported in the Azure portal after March 31, 2027, and will be available only in the Defender portal — build playbooks where they will live after that move.
Risks and limits: what automation will not do
SOAR handles predictable work. Novel attacks, insider cases, and decisions needing business context still need people, and any vendor suggesting otherwise is overselling. A bad playbook can also do damage at machine speed, isolating the wrong hosts or blocking legitimate traffic — so mature SOCs test playbooks in safe mode first, log every automated action, and keep a kill switch for each workflow.
Analysis: buy for your stack, automate the boring third first
Analysis — our assessment, not a vendor claim. The pattern that works is unglamorous: pick the platform closest to your existing SIEM and endpoint stack, automate enrichment and false-positive closure first, and keep containment behind human approval until the playbook has earned trust over weeks of clean runs. A practical first set is phishing triage, compromised-credential response, and malware-alert enrichment — high-volume, easy to measure, and a safe way to learn how playbooks behave before anything destructive is automated.
Frequently asked questions
What are cybersecurity automation tools for enterprise SOCs?
They are platforms, usually called SOAR tools, that connect a SOC’s security tools, enrich alerts with threat intelligence and asset context, and run repeatable response playbooks. They cut manual triage work and make incident handling consistent across analysts and shifts.
What is SOAR and how is it different from a SIEM?
A SIEM collects logs and detects suspicious activity; SOAR acts on it. SOAR stands for security orchestration, automation, and response: orchestration connects the tools, automation runs the repetitive steps, and response follows standardized playbooks. Most enterprise SOCs run both, with the SIEM feeding alerts into the SOAR platform.
Which SOAR tool is best for an enterprise SOC?
It depends on your existing stack. Cortex XSOAR suits large SOCs wanting the deepest playbook library, Splunk SOAR suits teams already standardized on Splunk, and Microsoft Sentinel suits Microsoft-centric estates. Shortlist two or three and test your own top playbooks before deciding.
How much do cybersecurity automation tools cost?
Enterprise SOAR pricing is usually quote-based, varying with seats and event volume, plus implementation and maintenance costs. Microsoft Sentinel is priced mainly on data ingested, with additional consumption charges possible for Logic Apps playbooks. Always budget for a playbook owner, because unmaintained automation loses value quickly.
What should a SOC automate first, and what should stay manual?
Automate enrichment, false-positive closure, and ticket creation first, since these are high-volume and low-risk. Keep destructive containment behind human approval until a playbook has proven reliable. Novel attacks and insider cases should always stay with human analysts.
Sources
- Comparitech — 6 Best SOAR Tools
- CybersecurityNews — Top 10 Best SOAR Tools in 2026
- Microsoft Learn — Automate threat response with playbooks in Microsoft Sentinel
- Palo Alto Networks — Cortex XDR Investigation and Response on Cortex XSOAR