AI Agent Deployment Explained: How to Put an AI Agent Into Production in 2026
Key takeaway: AI agent deployment turns a working agent demo into a live system real users can rely on. In 2026 there are five ways to do it — self-hosting, a managed agent runtime, serverless functions, a hosted agent app, or running locally — and the right choice depends on task length, data ownership, and who is on call when it breaks.
What AI agent deployment means
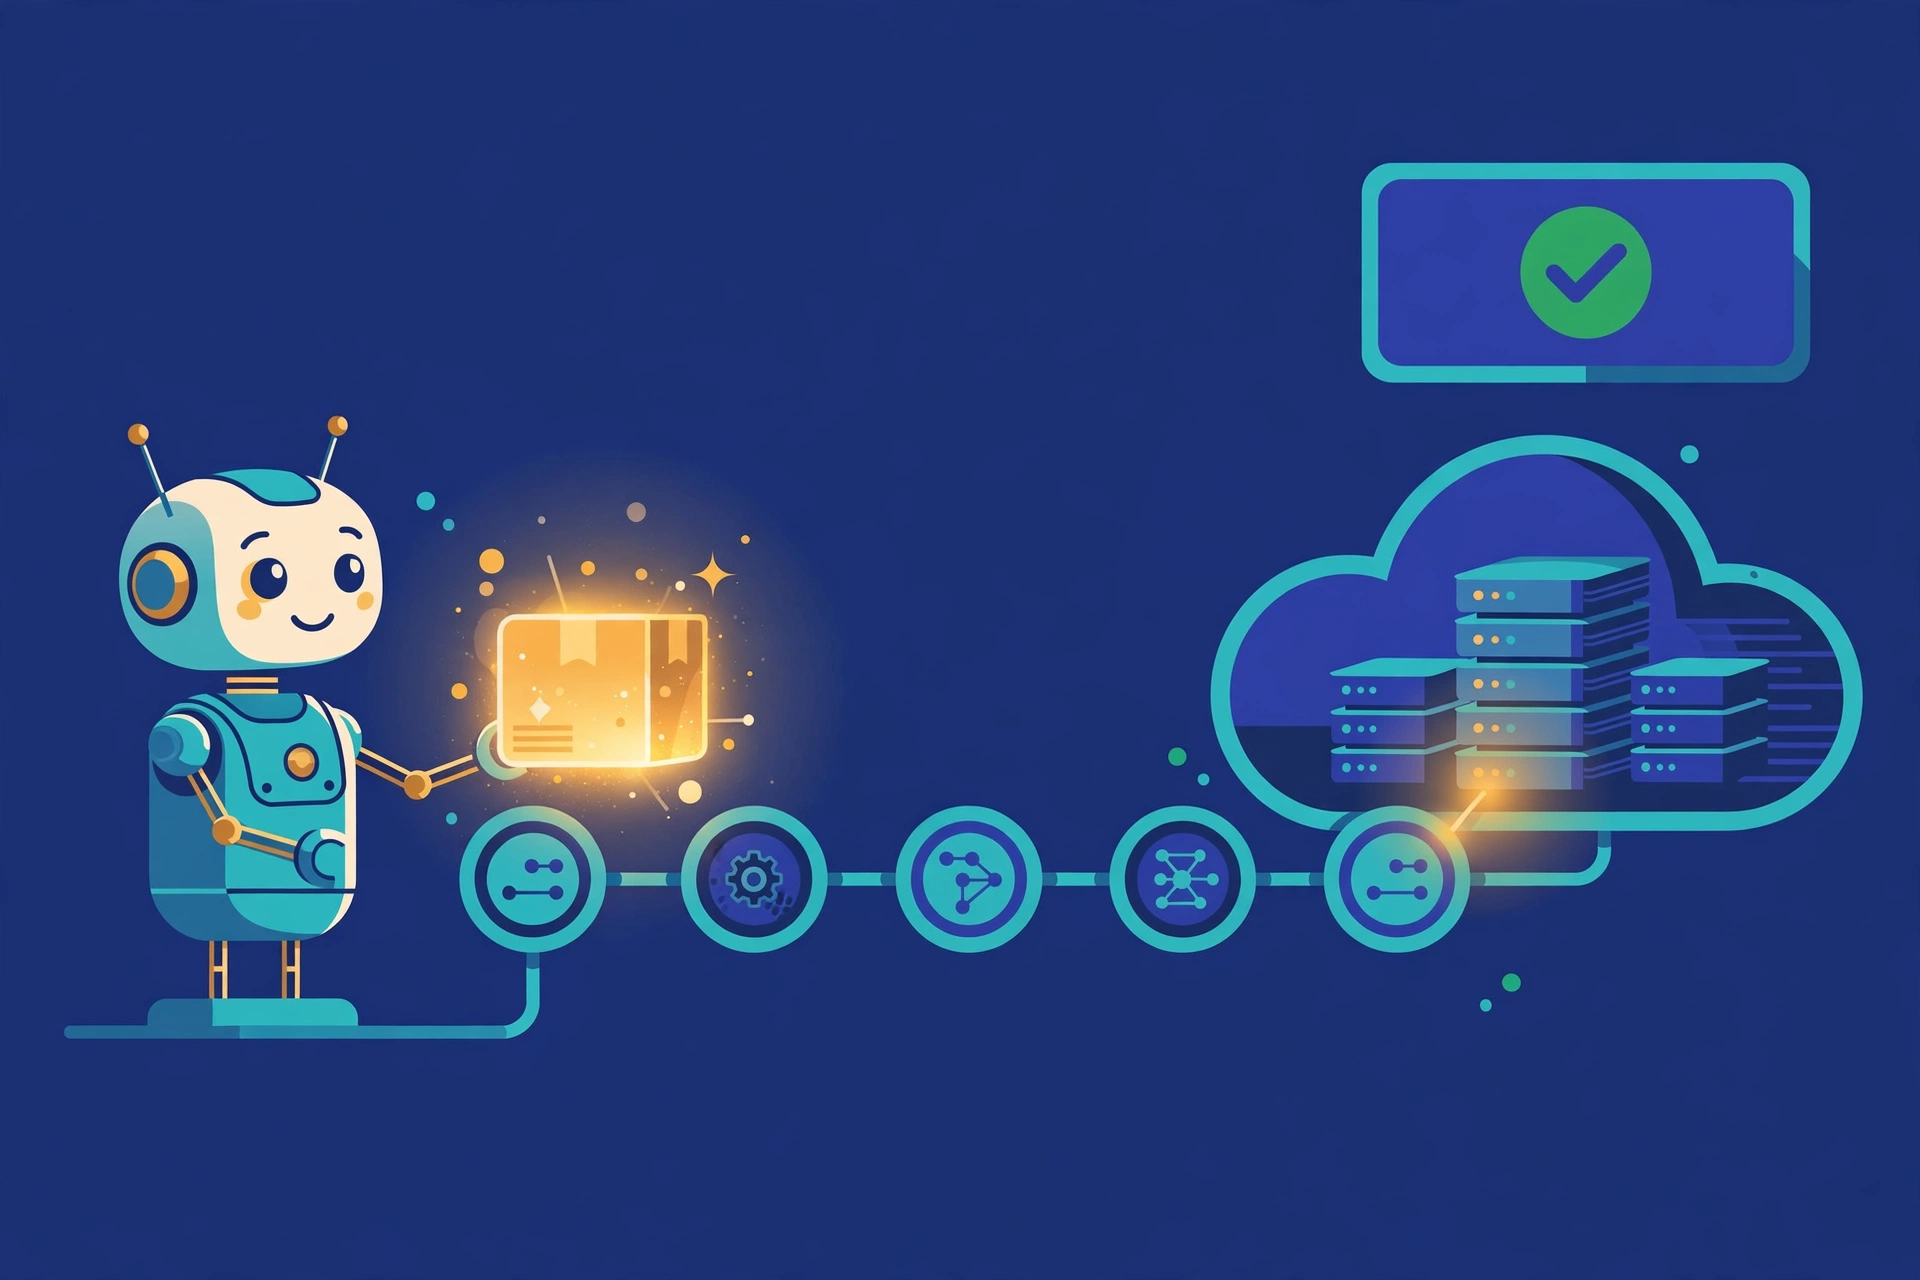
An AI agent takes a request, decides what to do, uses tools or data to act, and reports back. Building one in a notebook is the easy part. Deployment is everything after that: a place for it to run around the clock, memory to keep state between steps, access to the tools it needs, limits on what it can touch, and logs so you can see what it did. The jump from demo to production is where most agent projects stall: Gartner predicted in June 2025 that over 40% of agentic AI projects will be cancelled by the end of 2027, citing escalating costs, unclear business value, and inadequate risk controls. A MIT NANDA study from July 2025 found only about 5% of organisations that evaluated enterprise-grade AI tools had reached production.
The five AI agent deployment methods
Every production setup in 2026 falls into one of five methods. Most teams end up with a hybrid — for example, a serverless trigger that starts a job on a managed runtime, with a human approving high-impact actions.
| Method | How it works | Best for |
|---|---|---|
| Self-hosted | You run a framework such as LangGraph, CrewAI, or AutoGen on your own servers or Kubernetes cluster. | Strict data rules or high volume, with engineers to run it. |
| Managed agent runtime | You write the agent; the cloud provider runs it — for example AWS Bedrock AgentCore Runtime, Google Agent Runtime, or Claude Managed Agents. | Most teams in 2026; fastest route to production. |
| Serverless / edge | Agent steps run as short functions, such as AWS Lambda or Cloudflare Workers, orchestrated as a state machine. | Short, bursty tasks that start and stop often. |
| Hosted agent app | You sign into a product that already runs agents, such as ChatGPT agent, and configure it. | Non-technical teams that want an agent without writing code. |
| Local / on-device | The agent runs on a laptop or device with a local model. | Private data that must never leave the device, or offline use. |
AI agent deployment: which method fits your team?
Three questions narrow the choice fast. First, how long does one task run? AWS Lambda functions stop at 15 minutes, while an AWS Bedrock AgentCore Runtime session can run for up to 8 hours, so long multi-step jobs rule out plain serverless. Second, who must own the data? Regulated work that cannot leave your cloud account points to self-hosting or a managed runtime inside your own account. Third, who is on call when the agent breaks at 2am? If nobody is, pick a managed runtime or hosted app, not a cluster you maintain yourself.
Managed runtimes have closed most of the gap with self-hosting. AWS Bedrock AgentCore Runtime runs each user session in its own dedicated microVM, ending it when the session finishes. Google’s Agent Runtime, part of its Gemini Enterprise Agent Platform, offers the same idea on Google Cloud. Anthropic’s Claude Managed Agents is still in beta and is not currently eligible for Zero Data Retention or HIPAA BAA coverage, which rules it out for some regulated work.
What does AI agent deployment cost?
Costs split into three parts: the model, the runtime, and the tooling around it. The model is usually pay-per-token, so a busy agent costs more than a quiet one. The runtime is a monthly platform fee or per-second compute. The tooling — orchestration, a database for state and logs, and monitoring — is the part teams most often forget to budget. As a concrete example, one published 2026 production stack pairs n8n Cloud at $20 a month, Supabase at $25 a month, and the Claude API on pay-as-you-go, putting a small agent at roughly $95–$195 a month. Token usage is the variable: routing simple decisions to a small model and escalating only hard cases to a large one is the most effective way to cut it.
How to deploy an AI agent: the steps
Before deploying, settle the prerequisites. The agent needs an identity of its own — not a shared employee login — with short-lived, scoped credentials and an audit log of every action. Its tools should be connected through MCP, the Model Context Protocol, now the standard way to link agents to tools and data; Anthropic donated it to the Linux Foundation’s Agentic AI Foundation in December 2025. Then follow this sequence:
- Define the scope in writing. What the agent may do, what it may never do, and which actions need a human to approve them.
- Pick the runtime using the three questions above: task length, data ownership, and who is on call.
- Connect tools through MCP with least-privilege credentials — short-lived tokens, not long-lived keys.
- Add state and logging. The agent must remember where a task stands and leave a record of every decision and tool call.
- Test in staging with real users before production, including failure cases: bad input, a tool going down, a runaway loop.
- Ship with a kill switch and a rollback so you can stop the agent and return to the previous version in minutes.
The risks and limits of deploying AI agents
The biggest risk is not the model — it is giving an agent too much access with too little oversight. The safest production pattern is to let the agent call a scoped API that only knows verbs like deploy, roll back, or create an environment, and to put a human or policy gate in front of production changes. Every action should land in an immutable audit log tied to the agent’s own machine identity. Cost is the second risk: an agent that loops, retries, or calls an expensive model for every small decision can run up a large token bill in a day, so set per-session spending caps and alerts before launch. The third is silent failure — an agent that returns a confident wrong answer is worse than one that errors out. Evaluate the agent offline before release and monitor tool-call accuracy live.
Analysis: deployment is the product now
Analysis: In 2025 the hard part of AI agents was getting a demo to work. In 2026 it is running one safely at scale — and every major cloud provider now sells a managed agent runtime. The teams that ship successfully are not the ones with the cleverest prompts; they are the ones that treated deployment as the product: scoped access, state, logs, evaluation, and a kill switch. If you cannot answer who is on call when your agent breaks, you are not ready to deploy it.
What is AI agent deployment?
AI agent deployment moves an AI agent from a demo or notebook into a live, reliable system. It covers hosting, state and memory, tool access, security, monitoring, and rollback – everything real users need to depend on the agent.
What is the easiest way to deploy an AI agent?
For most teams, a managed agent runtime: you write the agent and the cloud provider handles isolation, sessions, and scaling. AWS Bedrock AgentCore Runtime, Google Agent Runtime, and Claude Managed Agents are the main options in 2026. For no code at all, use a hosted agent app.
How much does it cost to deploy an AI agent?
A small production agent can cost roughly $95-$195 a month using a stack such as n8n, Supabase, and a pay-as-you-go model API, according to one published 2026 breakdown. The main variable is token usage, so costs rise with task volume and model size.
Can I deploy an AI agent without writing code?
Yes. Hosted agent apps and no-code builders let you configure an agent – its instructions, tools, and data – without writing code. You trade control for convenience, so this route suits internal tools and small tasks best.
What is the biggest reason AI agent deployments fail?
Gartner’s June 2025 forecast points to escalating costs, unclear business value, and inadequate risk controls as the main reasons over 40% of agentic AI projects may be cancelled by the end of 2027. The most common technical failure is broad access without scoped credentials, evaluation, and a human gate on high-impact actions.
Sources: Zentor — AI Agent Deployment Methods: How to Choose in 2026; Agent Harness — Production AI Agent Deployment; Cognival — Deploy AI Agents to Production: The 2026 Stack That Actually Works; QueryNow — Why AI Agents Fail in Production (Gartner forecast via Reuters, June 2025; MIT NANDA, July 2025). Related on USABite: AI Agents for Government, How Is Agentic AI Different From Earlier Forms of AI?, AI Agents for Business Automation, Cloud Infrastructure Automation Tools Explained.